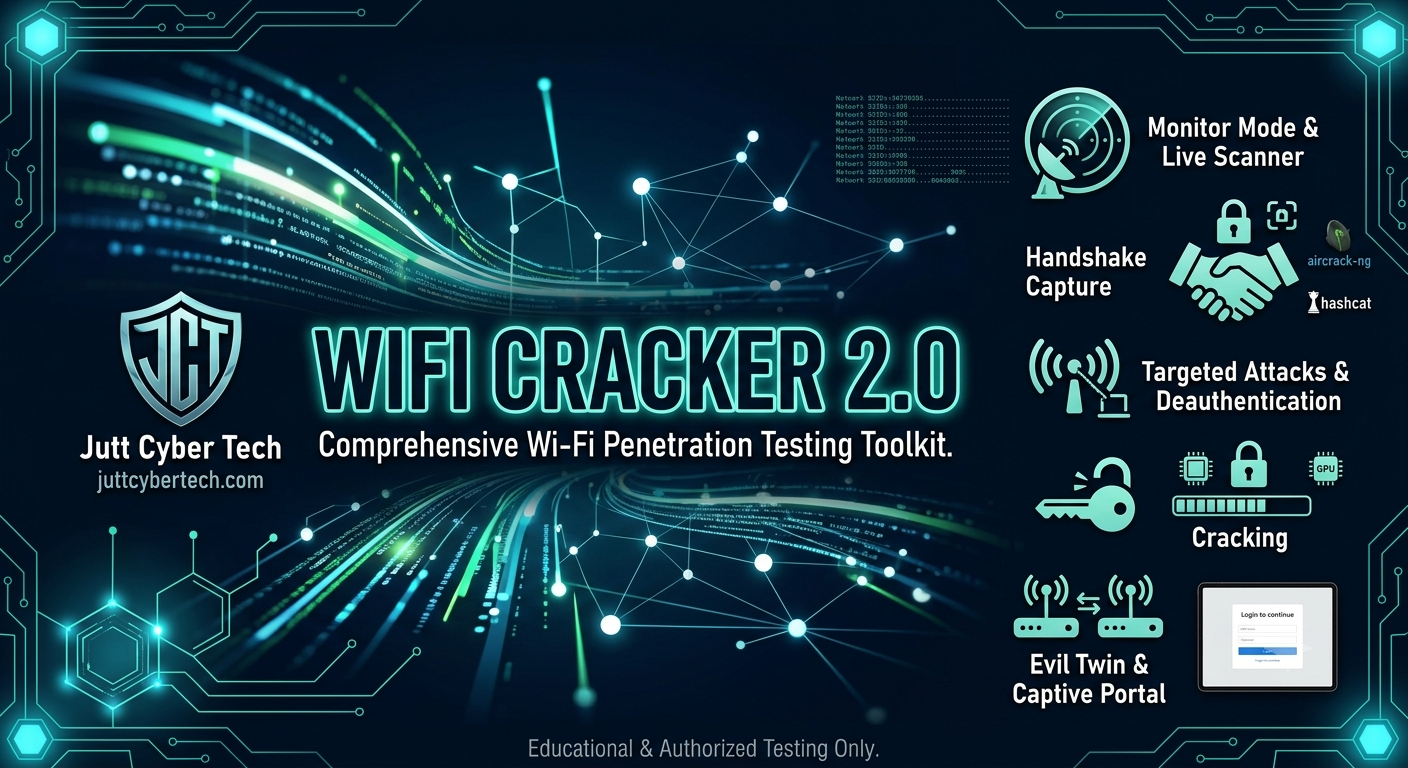
The next generation of wireless network auditing and security testing tools.
Designed for security professionals and ethical hackers, Wifi Cracker 2.0 provides advanced capabilities to identify vulnerabilities in wireless networks and ensure robust security configurations.
Rapidly discover available wireless networks, hidden SSIDs, and connected clients in your vicinity.
Vulnerability Analysis
Identify weaknesses in WEP, WPA, and WPA2 protocols to fortify your network defenses against intrusion.
High Performance
Optimized algorithms for faster auditing and testing with minimal resource consumption.
A comprehensive, menu-driven Wi-Fi penetration testing toolkit written in Go. This tool automates and simplifies the usage of powerful wireless security tools like aircrack-ng, hostapd, and hashcat, making complex attacks accessible through a user-friendly command-line interface.
Developed by Jutt Cyber Tech.
Disclaimer
This tool is intended for educational and authorized security testing purposes only. Using this tool on networks without explicit permission is illegal and unethical. The developer assumes no liability for any misuse or damage caused by this program.
Core Capabilities
System & Card Info
View detailed diagnostic information about your system hardware and underlying wireless network interface cards (NICs) to ensure compatibility.
Monitor Mode
Seamlessly toggle your wireless interfaces in and out of monitor mode to prepare for packet injection and raw traffic capturing.
Live Reconnaissance
Network Scanner
Scan for nearby access points in real-time utilizing airodump-ng, uncovering hidden SSIDs and network details.
Targeted Attacks
Isolate specific networks to view actively connected clients, then execute precise deauthentication attacks to forcibly disconnect them.
Handshake Operations
Automated capturing of WPA/WPA2 4-way handshakes
CPU-based cracking via aircrack-ng
GPU-accelerated cracking via hashcat for high-speed resolution
Hardware Requirements
Monitor Mode Adapter
To use Wifi Cracker 2.0 for capturing handshakes and performing deauthentication attacks, you need a wireless adapter that supports monitor mode and packet injection.
Once installed, you can launch the tool immediately:
sudo wifi-cracker
Method 2: From Source (For developers)
For users who want to build the program from the source code. You will need git and go (version 1.18 or newer) installed.
# 1. Clone the repository
git clone https://github.com/juttcybertech/WIFI-CRACKER-2.0.git
cd WIFI-CRACKER-2.0

# 2. Build the Go binary
go build -o wifi-cracker main.go

# 3. Move the binary to your PATH
sudo mv wifi-cracker /usr/local/bin/
3
Run the Program
Once installed, you can run the program from any directory using the following command. It requires sudo because it needs to manage network interfaces and run privileged tools.
sudo wifi-cracker
License
This project is licensed under the MIT License. See the LICENSE file for details.